Agent Observability Is Not Agent Accountability
Agent Observability Is Not Agent Accountability
Assumption to Challenge
Leaders increasingly assume a detailed agent trace is an audit trail. It may show a model call, a selected tool, and the sequence of steps. That is useful evidence about the run. It does not, by itself, prove which identity authorized a consequential cloud action, which policy allowed it, or what changed.
The distinction matters: visibility into behaviour is not the same as accountability for effect.
Why It Breaks Now
Agent observability is becoming more capable. AWS CloudWatch Omni describes traces, spans, and sessions for agent runs, including tool calls and model activity. OpenTelemetry's GenAI semantic conventions give teams a shared vocabulary for spans, metrics, and events. These advances make agent behaviour easier to observe and inspect.
But a tool span and a cloud API audit event belong to different layers. AWS CloudTrail's userIdentity element within an event identifies the IAM identity that made the request and, when available, associated credential metadata. The event also records the service and API action. A trace can explain why an agent attempted a tool call; the cloud event shows which identity made a request, not necessarily which agent run or approval led to it. Neither record alone necessarily establishes the full chain between user intent, agent run, approval, authorization, and cloud effect.
OWASP's 2025 Top 10 for Agentic Applications highlights tool misuse and identity or privilege abuse. NIST's AI Risk Management Framework is voluntary guidance, not a mandate, but it reinforces the broader point: managing AI risk spans design, use, and evaluation. Better dashboards do not settle who owns an action when those records remain disconnected.
Strategic Reframe
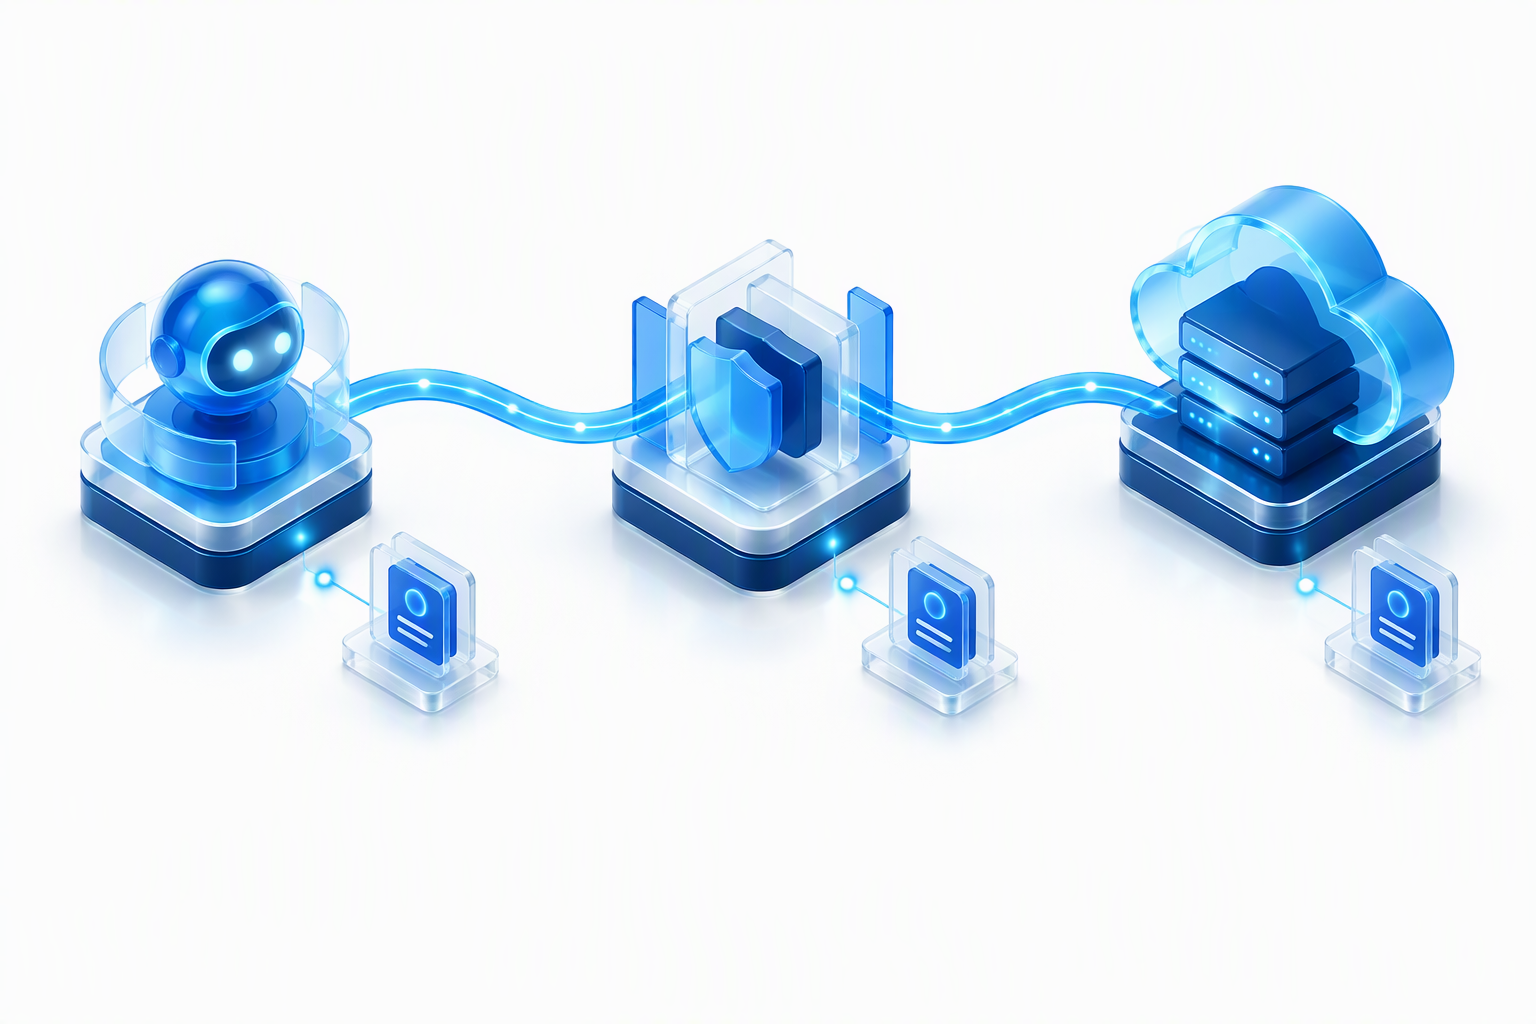
Thesis: For high-impact actions, observability supports accountability when the agent trace is deliberately joined to the acting identity, authorization decision, and resulting cloud event.
That join is a platform responsibility, not an observability-vendor indictment. A trace and a cloud audit log answer different questions; teams must deliberately correlate them. A timestamp match is not enough when identities are shared or workflows run concurrently. The evidence chain needs deterministic, scoped identifiers that travel across the agent run, authorization decision, and effect record. This linkage establishes provenance; it does not, by itself, prove causal execution or replace runtime authorization controls.
Decision Choices and Trade-offs
One path is to buy better agent dashboards while leaving trace data, identity records, approvals, and cloud events in separate systems. That limits integration cost and can improve debugging quickly. During an incident, however, teams must reconstruct provenance and sequence manually, and ownership can disappear between platform and application boundaries.
The alternative is an evidence contract for high-impact actions: define the identifiers, identity and policy fields, effect metadata, accountable owner, and retention rules required to reconstruct a run. This takes instrumentation and coordination. It also creates privacy risk if teams retain full prompts, tool payloads, or outputs indiscriminately. The contract should preserve enough provenance to review the decision while minimizing sensitive content and setting access and deletion boundaries.
These choices are not observability versus security. They are inexpensive visibility now versus evidence that can withstand an operational or governance review later.
Recommended Stance and First Executive Move
Make cross-layer evidence correlation a requirement for high-impact agent actions, alongside runtime approval and least-privilege controls. Do not collect everything by default. Record a deterministic join key, the responsible user or workload identity, the policy or approval outcome, and the cloud action and result; retain content only when its review value justifies its exposure.
This week, select one agent action that can alter production state. Ask platform, identity, security, and application owners to reconstruct its trace, principal, authorization or approval decision, and resulting cloud audit event. If a timestamp is the only link, or no team owns the missing link, record that as a control gap and assign an owner.
Brewed Insight
A trace explains what an agent did. Accountability starts when teams can trace its effects—and state exactly where the evidence stops.
Sources
- AWS, "Introducing Amazon CloudWatch Omni: AI-powered observability for generative AI and agentic workloads."
- Amazon CloudWatch Documentation, "Monitor AI agents."
- AWS CloudTrail Documentation, "Event record contents" and "userIdentity element."
- OpenTelemetry, "Semantic Conventions for Generative AI."
- OWASP GenAI Security Project, "Top 10 Risks and Mitigations for Agentic AI Security."
- NIST, "AI Risk Management Framework."