When AI Finds More, Verified Fixes Matter Most
When AI Finds More, Verified Fixes Matter Most
Assumption to Challenge
Finding more vulnerabilities automatically makes an organisation safer. Discovery matters, but a candidate report is not a remediated exposure. If review queues grow while fixes remain unverified, a higher scan count can make the programme look busier without reducing the risk that matters.
The opposite conclusion is no better: suppressing discovery because teams are busy leaves blind spots in place. The executive question is whether the organisation can turn credible findings into safer systems without losing sight of what it has not assessed.
Why It Breaks Now
Recent frontier-AI security research makes the handoffs harder to ignore. Microsoft’s FORGE Lab reports that, from May through September 2026, it helped address 140 CVEs and submitted 155 internally validated reports across 23 open-source projects. Those are Microsoft-reported results from a specific programme, not an enterprise baseline. The same account argues that repeatable discovery shifts pressure toward reproducibility, de-duplication, review capacity, and remediation.
That is different from the vendor-patch workload. Microsoft’s October 6 CISO perspective separately described close to 1,000 vulnerabilities in its September 2026 Patch Tuesday release. A supplier’s patch volume and an organisation’s own scanner findings have different sources and response paths; neither number should be passed off as a universal AI-driven enterprise trend. Google Threat Intelligence Group also describes one AI-discovered vulnerability later exploited after disclosure, while explicitly calling it an early indicator rather than an established pattern. For an organisation running an exposed product with a validated flaw, the response question is whether prioritisation and patch deployment reduce the exposure window; this single case does not establish how often such delays occur.
Strategic Reframe
Thesis: When AI-assisted discovery increases candidate volume, the durable security advantage is not discovery restraint; it is converting validated, contextually prioritized findings into verified risk reduction without losing sight of what remains undiscovered.
NIST’s enterprise patch-management guidance describes a lifecycle that includes prioritising, installing, and verifying fixes. That general guidance is not an AI-specific mandate, but it captures the strategic point: deployment is not complete when a change is merely scheduled. Teams need evidence that the exposure is addressed.
Decision Choices and Trade-offs
Leaders can optimize discovery output, or manage the response system around it. More scanning can reveal weaknesses sooner; poorly supported or duplicate findings can consume scarce attention. Faster changes can reduce exposure, while untested changes can disrupt critical services. These are not reasons to pause discovery. They are reasons to pair it with evidence quality, asset context, clear ownership, and safe verification.
The path differs by finding. A defect in first-party code may wait on reproduction, developer capacity, and review. A vendor patch may wait on compatibility assessment, staging, and a production window. Combining both into one queue hides where work is actually stuck. Prioritization should reflect severity, exposure, confidence in the evidence, duplication, and the cost of delaying a fix. That is an executive decision frame, not a universal scoring formula.
Recommended Stance and First Executive Move
Keep discovery open; govern response with risk-proportionate validation, de-duplication, and asset context. Measure verified risk reduction alongside unresolved findings and observable visibility gaps—such as assets not inventoried or dependencies not assessed. Do not pretend the unknown vulnerability population itself can be counted.
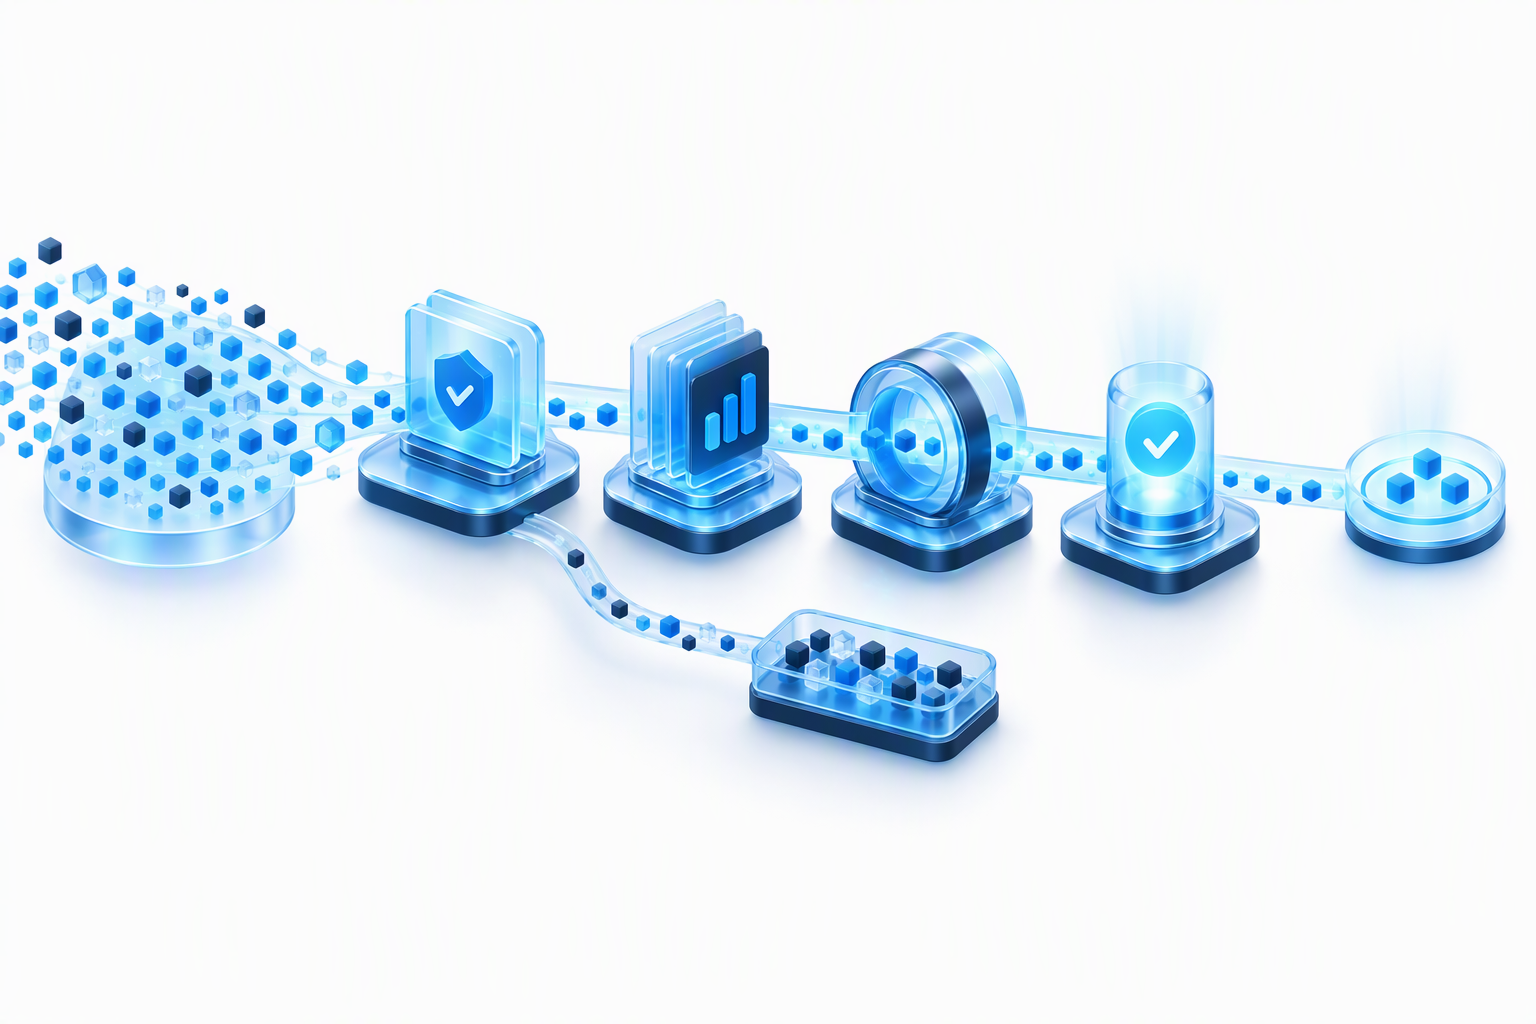
Next week, choose one externally exposed, high-impact service. Trace a representative finding from candidate report through validation, owner, fix, deployment, and verification, then check observable coverage gaps such as dependencies without a current assessment or a named owner. Identify the slowest handoff and assign an owner. Treat this as a diagnostic sample, not an enterprise-wide estimate; shared and orphaned components may expose different gaps.
Brewed Insight
Discovery tells you where to look. Security improves when the organisation can prove what matters, fix it safely, and verify the exposure is gone.
Sources
- Microsoft Security, "3 lessons from frontier AI vulnerability research."
- Microsoft Security, "CISO perspectives on managing vulnerability risks in the age of AI."
- Google Cloud Threat Intelligence Group, "Vulnerability discovery and exploitation trends in the AI era."
- NIST, "Guide to Enterprise Patch Management Planning: Preventive Maintenance for the Enterprise," SP 800-40 Rev. 4.